The stability of global enterprise infrastructure relies on a single logical hierarchy: the Domain Name System (DNS). Behind every microservice call, edge routing rule, and TLS certificate exchange sits a complex system of administrative policies, legal frameworks, and technical standards that map human-readable domain names to numeric IP addresses.
Understanding how this governance system evolved from early informal agreements to today’s multi-stakeholder model provides crucial context for systems architects, IT decision-makers, and network engineers managing high-availability Web property portfolios.
The Genesis of Root Oversight: Centralization to Fragmentation
In the early days of the ARPANET and the nascent Internet, central registry operations belonged to a single individual: Jon Postel. Operating as the Internet Assigned Numbers Authority (IANA) at the Information Sciences Institute (ISI) at the University of Southern California, Postel managed top-level assignments, IP allocations, and protocol parameters manually via plain-text files.
[ RFC 748 / Informal Postel Management ]
                   │
                   ▼
[ Network Solutions, Inc. (NSI) Monopoly ]
 (NSF Contract / Commercialization)
                   │
                   ▼
[ gTLD-MoU Memorandum of Understanding ]
 (IAHC / Early Multi-Stakeholder Attempt)
                   │
                   ▼
[ Formation of ICANN (1998) ]
 (US Department of Commerce Oversight)
                   │
                   ▼
[ IANA Stewardship Transition (2016) ]
 (Global Multi-Stakeholder Model)
As commercial interest surged in the early 1990s, the National Science Foundation (NSF) contracted Network Solutions, Inc. (NSI) to manage registration functions for non-military top-level domains like .com, .org, and .net. This created a commercial monopoly over global root management that quickly led to administrative bottlenecks, legal challenges over trademark rights, and international concern regarding US-centric control of global critical infrastructure.
The gTLD-MoU Framework: The Early Multi-Stakeholder Experiment
By 1997, international organizations, technical bodies, and telecommunication operators recognized that a single commercial entity should not control the expansion of the Internet’s namespace. The Internet Society (ISOC) and the Internet Architecture Board (IAB) established the International Ad Hoc Committee (IAHC) to engineer a competitive, internationalized framework for domain administration.
This effort produced the generic Top-Level Domain Memorandum of Understanding (gTLD-MoU). The gTLD-MoU was an ambitious international treaty-like framework designed to achieve several structural goals:
- Registry-Registrar Separation: Disentangling the underlying database operator (registry) from consumer-facing sales agents (registrars) to spark commercial competition.
- Namespace Expansion: Adding seven new gTLDs (
.arts,.firm,.info,.nom,.rec,.store,.web) to relieve pressure on the overburdened.comnamespace. - Administrative Dispute Resolution: Establishing early administrative mechanisms to handle trademark infringement, laying the groundwork for what later became the Uniform Domain-Name Dispute-Resolution Policy (UDRP).
- Council of Registrars (CORE): Creating a Swiss-based non-profit association of global registrars to manage allocations cooperatively.
Why the gTLD-MoU Shifted Strategy
Despite its technical foresight, the gTLD-MoU struggled with geopolitical hurdles. The United States government, particularly the Department of Commerce (DoC), balked at delegating critical Internet root control to an international consortium led by telecom bodies and foreign organizations without explicit US policy oversight.
In June 1998, the US Department of Commerce issued its Statement of Policy (commonly referred to as the “White Paper”), calling for a private, non-profit corporation based in the US to assume oversight of the Domain Name System. This directive effectively ended the gTLD-MoU era and paved the way for the creation of ICANN.
The Architecture of ICANN: Building the Modern Multi-Stakeholder Model
Incorporated in California in late 1998, the Internet Corporation for Assigned Names and Numbers (ICANN) assumed responsibility for coordinating the Internet’s unique identifiers. Rather than functioning as a traditional governmental regulatory agency, ICANN operates via a bottom-up, multi-stakeholder consensus model.
                           ┌──────────────────────────┐
                           │   ICANN Board of         │
                           │     Directors            │
                           └─────────────┬────────────┘
                                         │
         ┌───────────────────────────────┼───────────────────────────────┐
         │                               │                               │
         ▼                               ▼                               ▼
┌──────────────────┐           ┌──────────────────┐           ┌──────────────────┐
│ GNSO             │           │ ccNSO            │           │ ASO              │
│ Generic Names    │           │ Country Code     │           │ Address          │
│ Supporting Org   │           │ Supporting Org   │           │ Supporting Org   │
└────────┬─────────┘           └──────────────────┘           └──────────────────┘
         │
 ┌───────┴───────────────────────┐
 │                               │
 ▼                               ▼
┌──────────────────┐   ┌──────────────────┐
│ Registries       │   │ Registrars       │
│ Stakeholder Group│   │ Stakeholder Group│
└──────────────────┘   └──────────────────┘
ICANN’s policy-making engine relies on distinct Supporting Organizations and Advisory Committees that represent different technical, commercial, and geopolitical interests:
1. Generic Names Supporting Organization (GNSO)
Develops policy for generic Top-Level Domains (.com, .cloud, .app). The GNSO is split into commercial and non-commercial stakeholder groups, housing both domain registries and accredited registrars.
2. Country Code Names Supporting Organization (ccNSO)
Handles policies relating to two-letter country-code TLDs (.uk, .de, .jp). Country code operators retain significant sovereign autonomy, interacting with ICANN primarily around global root zone stability.
3. Governmental Advisory Committee (GAC)
Composed of representatives from national governments and multinational public authorities. The GAC advises the ICANN Board on public policy issues, trademark protections, and sovereign digital rights.
4. Root Server System Advisory Committee (RSSAC) & Security and Stability Advisory Committee (SSAC)
Provides technical oversight, risk assessment, and operational guidance to safeguard the structural resilience of the 13 root server IP clusters.
Structural Evolution: gTLD-MoU vs. ICANN
Comparing early administrative attempts with mature ICANN frameworks highlights how domain name management shifted from experimental international treaties to formal, legally binding commercial and technical oversight:
| Structural Dimension | gTLD-MoU Framework (1997) | Modern ICANN Framework (Present) |
| Legal Authority | Multi-party Memorandum of Understanding (Swiss Law focus) | California Non-Profit Public Benefit Corporation |
| Enforcement Mechanism | Voluntary compliance & cooperative registrar agreements | Legally binding Contracts (RAA, Registry Agreements) |
| IANA Control | Proposed transition to international bodies (ITU, ISOC) | Post-2016 IANA Stewardship Transition (PTI under public oversight) |
| Dispute Resolution | Early proposed administrative panels | Standardized UDRP and URS policies across all gTLDs |
| Namespace Expansion | Rigid, static addition of 7 fixed TLDs | New gTLD Program (1,200+ delegate domains, IDNs, brands) |
| Root Zone Security | Unsigned plain-text zone file generation | Globally enforced DNSSEC signing and automated key rollover |
Key Milestone: The 2016 IANA Stewardship Transition
For the first eighteen years of ICANN’s existence, the US National Telecommunications and Information Administration (NTIA)—an agency of the US Department of Commerce—retained final authority over changes to the authoritative Root Zone File. This historical arrangement meant the US government possessed technical veto power over root delegations.
On October 1, 2016, the NTIA officially allowed its contract with ICANN to expire. Control of the IANA functions transferred to Public Technical Identifiers (PTI), a purpose-built affiliate of ICANN governed directly by the global Internet community.
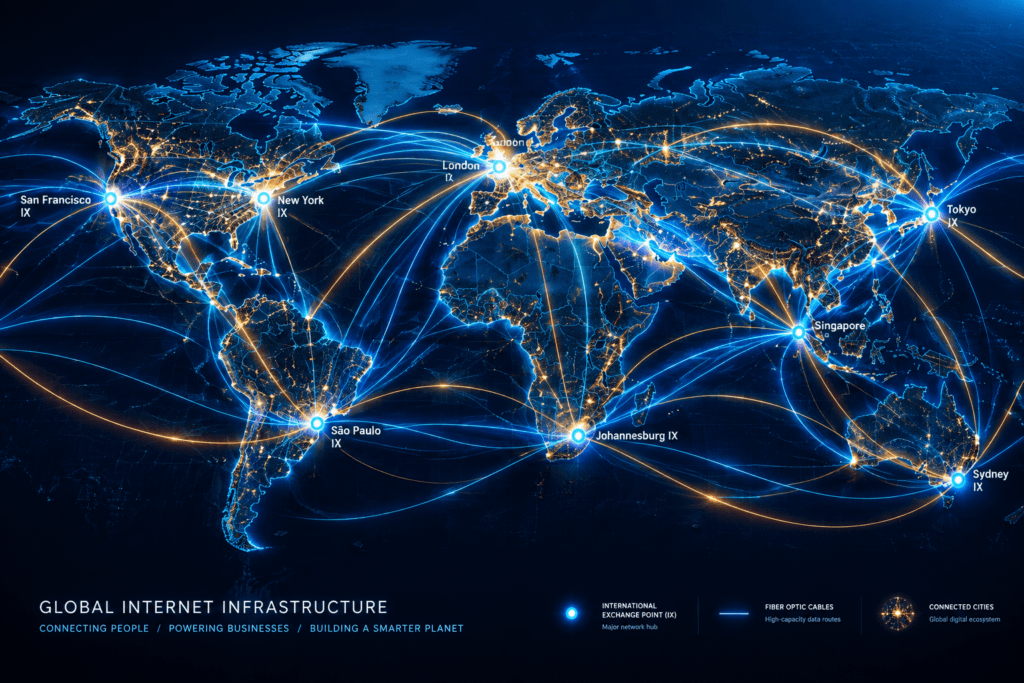
This transition reinforced a key principle of enterprise web infrastructure: no single government or commercial entity owns or controls the root zone of the global DNS. Technical consensus, operational auditing, and peer-reviewed RFC standards govern root modifications.
Technical Implications for Enterprise Infrastructure Teams
For systems administrators, enterprise architects, and site reliability engineers (SREs), domain governance directly impacts daily operational security, resilience, and compliance.
+-----------------------------------------------------------------------------------+
|                        ENTERPRISE DOMAIN MANAGEMENT STACK                          |
+-----------------------------------------------------------------------------------+
| Policy Layer       | ICANN Consensus Policies, UDRP, Registry Agreements          |
+--------------------+--------------------------------------------------------------+
| Commercial Layer   | Registrar Accreditation Agreement (RAA), ICANN-Accredited   |
|                    | Enterprise Registrars, EPP Lock Controls                     |
+--------------------+--------------------------------------------------------------+
| Protocol Layer     | Extensible Provisioning Protocol (EPP), DNSSEC Key Management|
|                    | Registry-Registrar Thick/Thin Database Synchronization       |
+--------------------+--------------------------------------------------------------+
| Operational Layer  | Authoritative DNS Anycast Networks, Edge Routing, TLS Auth   |
+-----------------------------------------------------------------------------------+
1. Extensible Provisioning Protocol (EPP) Standardization
The separation of registries and registrars under ICANN led directly to the development of EPP (RFC 5731-5734). EPP provides a secure, transactional protocol for managing domain objects, host objects, and contact records across disparate infrastructure platforms. Enterprise domain management automation depends entirely on standardized EPP commands (<create>, <update>, <transfer>, <renew>).
2. DNSSEC Implementation & Chain of Trust
Root governance ensures the cryptographic integrity of the Root Key Signing Key (KSK). Enterprise networks deploying Domain Name System Security Extensions (DNSSEC) rely on this authoritative anchor to validate signature chains down to local zones (.com → example.com), mitigating cache poisoning and Man-in-the-Middle (MitM) attacks across corporate routing environments.
3. Registry-Registrar Security Protocols
Modern ICANN Registrar Accreditation Agreements (RAA) enforce operational safeguards critical for protecting enterprise domain portfolios against unauthorized transfers and hijacking:
- EPP Transfer Locks (
clientTransferProhibited): Prevents unauthorized domain transfers at the registry level. - Registrant Verification: Mandatory contact updates to prevent administrative forfeiture.
- Multi-Factor Authentication & IP Allowlisting: Enforced at the registrar API layer to protect mission-critical DNS zone delegations.
Preparing for the Next Phase of Domain Name Governance
Domain name governance continues to evolve alongside shifting technical demands and regulatory landscapes. Organizations managing complex web infrastructure should align their long-term digital asset strategies with upcoming developments in root oversight:
- The Next Application Window for New gTLDs: ICANN is preparing subsequent rounds of the New gTLD Program, allowing enterprises to apply for custom dot-brand top-level domains (
.brand) to unify their global digital footprint and control top-level routing policies internally. - Data Privacy vs. WHOIS Transparency: Regulatory frameworks like the EU’s GDPR and California’s CCPA prompted ICANN to replace traditional public WHOIS lookup systems with the Registration Data Access Protocol (RDAP). Enterprise teams must update automated threat intelligence platforms that rely on WHOIS scraping to query RDAP endpoints securely using authenticated access models.
- DNS-over-HTTPS (DoH) and DNS-over-TLS (DoT): As transport-level encryption for DNS queries moves from client devices to recursive resolvers, governance discussions are expanding to address resolver centralisation, content filtering compliance, and zero-trust corporate security architectures.
Proactively tracking ICANN policy updates, maintaining registry-level security locks, and auditing trust anchors across enterprise DNS infrastructure ensures that critical web applications remain secure, accessible, and resilient against global network disruptions.